
Industry Portal
Related News
- 00
0000-00
How to Specify Low-Pressure Casting Parts for Leak-Tight Automotive Housings - 00
0000-00
How to Specify an Electric Sunroof for Passenger Cars: Key Design and Safety Factors - 00
0000-00
North American Vehicle Aesthetics: Trends Shaping Exterior Design and Materials - 00
0000-00
ASPICE for Smart Optical Systems: Evidence Needed for Automotive Development - 00
0000-00
How to Select NVH Control Materials for Automotive Panels and Powertrain Systems
Automotive Sensor Systems and ISO 26262: What to Review for Functional Safety Compliance
Why does automotive sensor systems ISO 26262 review matter now?
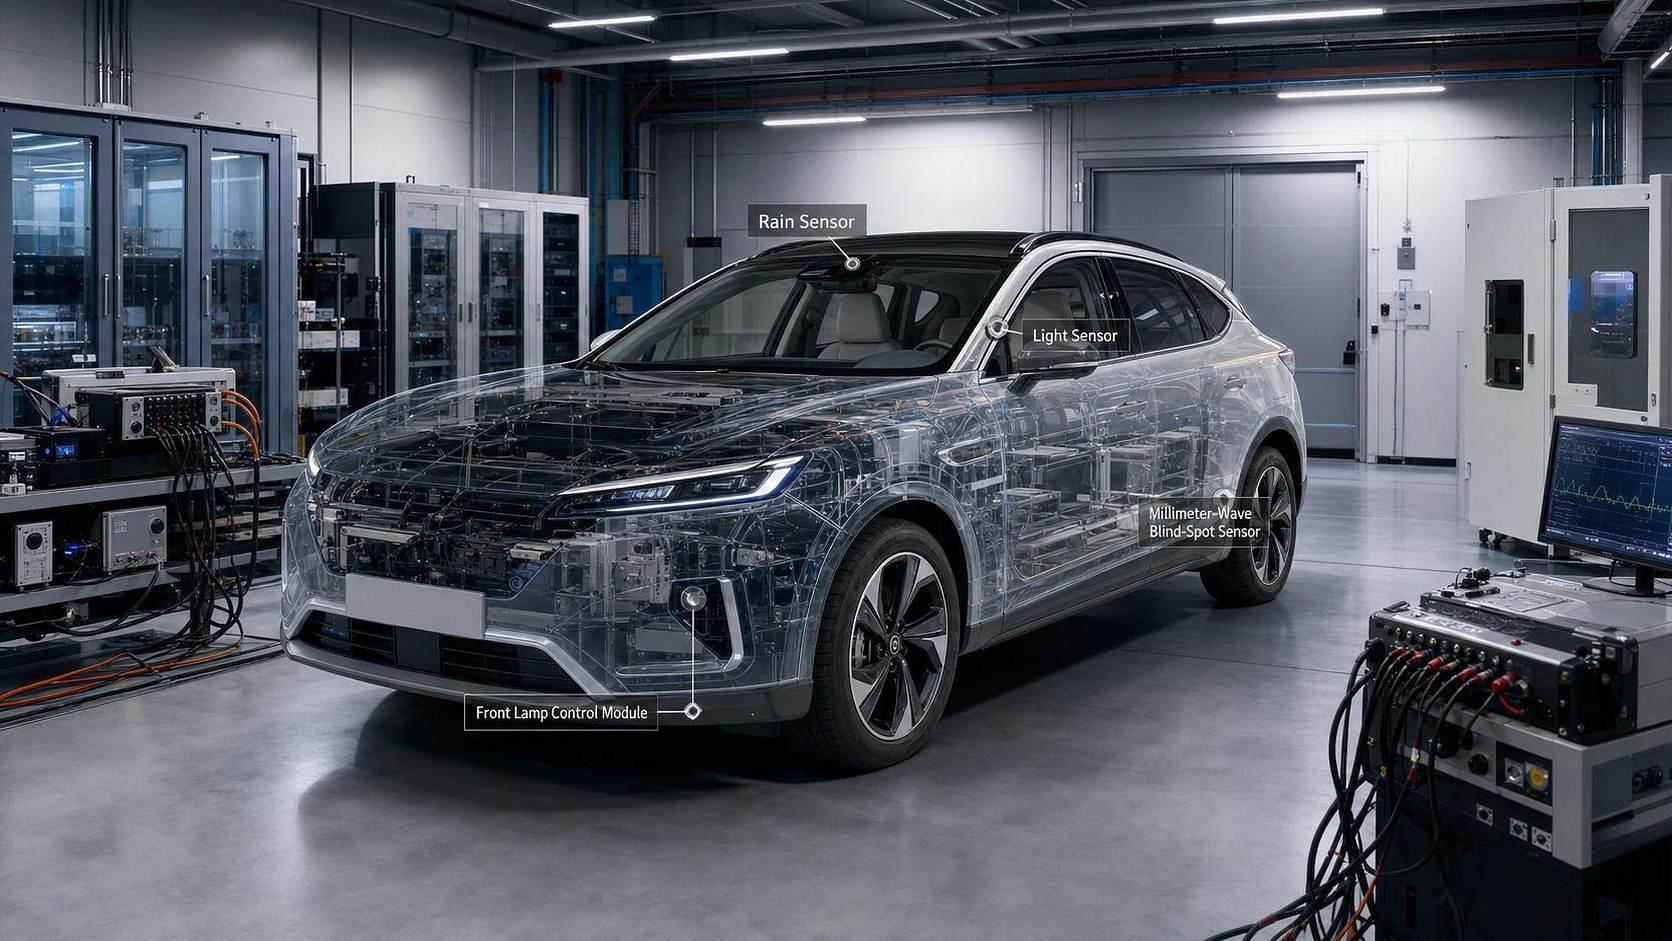
Vehicle intelligence now depends on sensors far beyond core ADAS modules.
Exterior lighting, rain detection, blind-spot support, auto headlight activation, and body sensing all influence safety-related behavior.
That is why automotive sensor systems ISO 26262 review has moved from a specialist concern to a routine compliance task.
In practical terms, the standard asks a simple question.
If a sensor fails, drifts, freezes, or sends a misleading signal, can the vehicle remain acceptably safe?
For exterior and vision systems, that question becomes more complex in EV platforms.
Higher software content, tighter energy targets, and integrated body electronics create more hidden dependencies than many teams expect.
AEVS follows this shift closely because smart exterior components no longer sit at the edge of vehicle development.
They influence driving perception, aerodynamic packaging, optical performance, and regulatory readiness at the same time.
A functional safety review therefore is not only about passing an audit.
It helps prevent weak assumptions from entering sourcing, validation, and release decisions.
What exactly should be reviewed under ISO 26262 for sensor systems?
A common mistake is to review only the sensor hardware.
ISO 26262 expects a wider view that includes the full safety path.
That path usually starts with sensing, but it continues through signal processing, decision logic, communication, diagnostics, and fault reaction.
For automotive sensor systems ISO 26262 work, the review often covers these checkpoints:
- Item definition and system boundaries, including interfaces with body controllers, lighting ECUs, and gateway modules.
- Hazard analysis and risk assessment, especially for loss, corruption, delay, or unintended activation.
- Safety goals and technical safety requirements assigned to hardware and software elements.
- Diagnostic coverage, fault detection timing, and transition to a safe state.
- Verification evidence, including fault injection, environmental tests, and interface validation.
The review should also examine assumptions borrowed from legacy platforms.
For example, a rain sensor used only for comfort features may receive different scrutiny than one linked to visibility support logic.
The same part can fall into a different safety discussion once system context changes.
A quick judgment table for review focus
The table below helps sort where compliance effort usually needs to go first.
Which sensor applications deserve the closest attention?
Not every sensor carries the same safety weight.
The closer a function is to visibility, motion judgment, or automated intervention, the more carefully automotive sensor systems ISO 26262 should be reviewed.
In exterior and vision architectures, several applications regularly trigger deeper review.
- Photoelectric sensors tied to automatic headlamp control or glare management.
- mm-wave sensing used for blind-spot support or side perception.
- Rain and ambient light sensors that affect visibility-related functions.
- Sensor switches connected to body domain controllers with shared fault paths.
What raises concern is not only failure frequency.
It is also how difficult the failure is to detect before it shapes driver information or vehicle response.
For example, an obvious open circuit may be easier to control than a biased optical signal under unusual weather and road lighting.
AEVS often highlights this issue in smart headlight and optical perception discussions.
As matrix lighting becomes more interactive, the safety review must include optical algorithm behavior, not just the sensing element.
Where do teams usually fail an ISO 26262 sensor review?
Most failures are not caused by one missing document.
They come from gaps between engineering domains.
A sensor may be electrically sound, while the overall functional safety case remains weak.
Several patterns appear repeatedly.
The safety concept stops too early
Some reviews focus on detection but skip the system reaction.
A diagnostic trouble code is not enough if the vehicle behavior remains undefined after fault confirmation.
Environmental validation is treated as reliability only
Contamination, fogging, heat soak, and vibration often affect safety performance before they create a hard failure.
This is especially relevant for exterior sensors near lighting, wheels, or exposed body surfaces.
Supplier assumptions do not match vehicle use
A component may be developed for one ASIL assumption, then integrated into a more demanding architecture.
Without interface clarity, the compliance package looks complete but remains structurally weak.
Traceability becomes fragmented
If hazards, requirements, test cases, and anomalies are stored in separate workflows, review time expands quickly.
More importantly, unresolved contradictions can survive into release gates.
How should implementation, cost, and timing be judged realistically?
A useful automotive sensor systems ISO 26262 review is not only technical.
It must also test whether the compliance plan fits sourcing, validation, and launch timing.
In real programs, cost pressure often pushes teams to reuse sensors, software libraries, or diagnostics from earlier platforms.
Reuse can be valid, but only when assumptions are rechecked in the new item definition.
A practical review usually asks:
- Do the planned safety mechanisms require extra ECU resources or bus bandwidth?
- Will environmental and fault-injection testing extend DV or PV timing?
- Are supplier work products aligned with the expected safety case structure?
- Is there enough evidence for software updates after SOP?
The answer affects budget more than the sensor bill of materials alone.
For EV exterior systems, packaging and thermal interactions can also change validation scope.
A sensor near a high-output LED assembly or exposed wheel arch may need more than standard bench confirmation.
That is one reason market intelligence platforms like AEVS track both technical evolution and compliance context together.
What is a sensible next-step checklist before sign-off?
Before approval, it helps to reduce the review to a few high-value checks.
This keeps the process disciplined without turning it into a paperwork exercise.
- Confirm the sensor function in vehicle context, not only at component level.
- Recheck hazard assumptions against current software features and driver information logic.
- Verify that fault detection leads to a defined and validated safe response.
- Review environmental edge cases relevant to exterior placement and optical performance.
- Check traceability from safety goal to verification evidence and open issue closure.
- Confirm post-launch update handling where sensor logic can change through software.
Taken together, these steps make automotive sensor systems ISO 26262 review more credible and easier to defend.
They also help separate real safety risks from routine engineering noise.
The strongest compliance decisions usually come from early boundary definition, realistic fault thinking, and vehicle-level validation.
When sensor systems support visibility, perception, and body control together, isolated review is rarely enough.
The next useful move is to map each sensor function, its safety path, and its missing evidence before the next gate review.
That creates a clearer basis for design correction, supplier alignment, and release timing decisions.