
Industry Portal
Related News
- 00
0000-00
How to Evaluate a Photoelectric Sensing Supplier for Industrial Automation Projects - 00
0000-00
Automatic Wipers for Buses: 7 Selection Criteria for Fleet Procurement - 00
0000-00
How Smart Optical Perception Prevents Collisions in Low-Light Driving Conditions - 00
0000-00
Private Label Tire Export: Evaluating Suppliers, Compliance, and Landed Cost - 00
0000-00
DOT-Compliant Truck Lighting: A Practical Guide to FMVSS 108 Requirements
Tags
U.S. DOT Draft Rule Raises ADB Module Security Bar
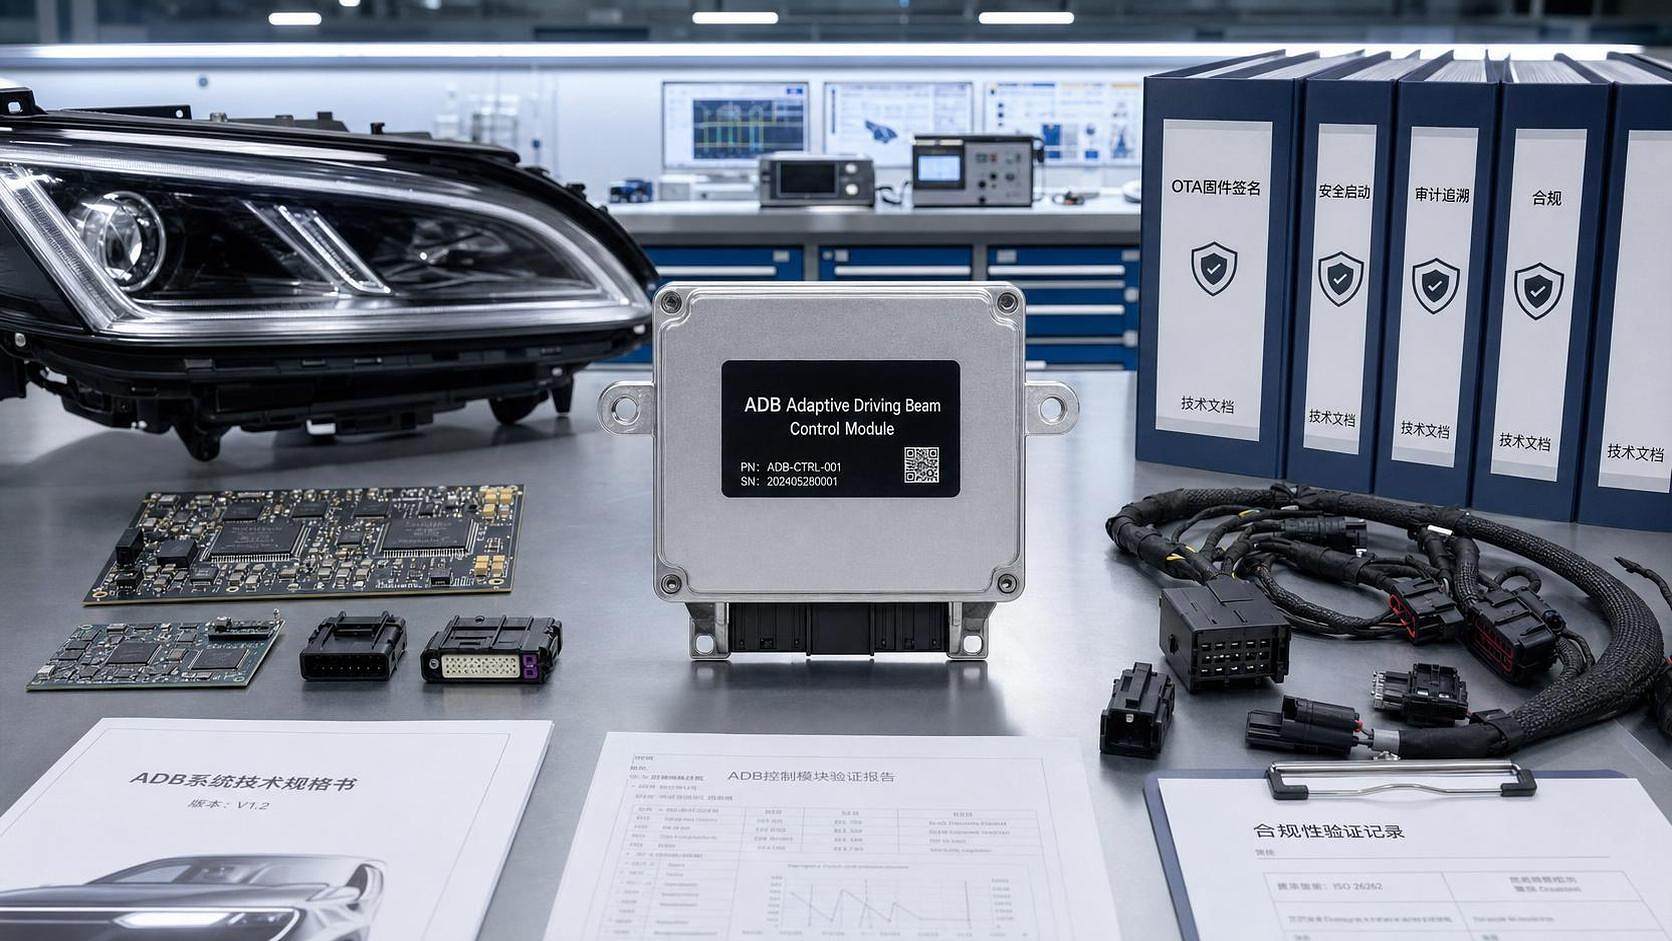
On January 1, 2027, this policy development is set to become a practical compliance issue for companies involved in adaptive driving beam (ADB) modules entering the U.S. market. Based on the draft notice released by NHTSA on June 20, 2026, the change is not only about product design, but also about how exporters, importers, procurement teams, and compliance functions prepare technical documentation, review delivery readiness, and assess whether existing ADB control modules can still meet import requirements.
What the draft notice clearly requires
The confirmed information available shows that NHTSA released the draft ADB Cybersecurity Framework Notice on June 20, 2026. The draft states that all imported ADB control modules from January 2027 must include a verifiable OTA firmware signature mechanism. It also requires suppliers to provide importers with Firmware Audit Log interface documentation. The information provided further indicates that this change is expected to raise export compliance requirements for Chinese ADB modules and affect shipments of existing mid- and low-end solutions that do not use a secure boot design.
Where the rule change may be felt first
Export-facing module suppliers may face a design compliance gap
From an industry perspective, the most direct pressure is likely to fall on manufacturers and exporters shipping ADB control modules into the U.S. market. The reason is straightforward: the draft requirement is tied to embedded security capability and supporting technical documentation, which means products without verifiable OTA signature design or without a usable audit-log interface description may face additional compliance review before shipment. What deserves closer attention is not only the hardware or firmware architecture itself, but also whether export documentation can demonstrate that the module meets the new security-related expectation.
Importers and procurement teams may tighten supplier screening
Analysis shows that importers are likely to pay closer attention to whether suppliers can provide firmware audit interface documents in a usable and reviewable form. In practice, that may affect supplier qualification, technical bid alignment, and model selection for future sourcing. For procurement teams, the issue is no longer limited to optical performance or cost positioning; firmware signing capability and traceability documents may become part of pre-shipment review and supplier comparison.
Compliance and certification-related functions may need earlier document checks
Observably, the draft points to a stronger documentation burden around firmware control and auditability. For compliance teams and service providers involved in technical review, the change may shift attention toward firmware signature mechanisms, interface descriptions, and product-level evidence that can support import review. Even where execution details are not yet fully stated in the input, companies should note that document readiness may become as important as the module’s functional specification.
After-sales and traceability roles may also be drawn into the process
Analysis shows that once firmware audit logging becomes part of the import-facing requirement, after-sales support and product traceability functions may also need adjustment. Suppliers may need to consider how firmware records, update history, and related interface information are retained and communicated across delivery and service stages, especially where importers request clearer audit support before or after shipment.
What companies should review now
Check whether current ADB platforms already support the required security logic
What deserves closer attention is whether existing ADB control modules already include a verifiable OTA firmware signing mechanism, especially in product lines aimed at price-sensitive shipments. If a current design lacks secure-boot-related architecture, the issue should be treated as a potential export readiness gap rather than only a future engineering upgrade topic.
Prepare firmware audit documentation for trade and compliance use
From an industry perspective, suppliers should pay close attention to the availability and completeness of Firmware Audit Log interface documentation. Even if the draft does not yet provide full execution detail in the input, import-facing documentation may become a practical checkpoint in customer review, customs-related preparation, or compliance file management.
Watch for changes in customer specifications and delivery conditions
Analysis shows that companies should monitor whether buyers, importers, or channel partners begin updating technical specifications, qualification questionnaires, or delivery terms in response to the draft notice. This matters because rule changes often begin affecting trade through procurement documents and acceptance requirements before broader market practice becomes stable.
Reassess supplier capability and delivery timing
Observably, where a supplier still relies on existing designs without secure boot or related firmware verification capability, lead times, redesign schedules, and model continuity may become points of concern. Companies involved in sourcing or export planning should therefore review whether supplier qualification, replacement planning, and delivery commitments remain aligned with the expected January 2027 requirement window.
Why this matters more as a compliance signal than a finished outcome
Analysis shows that this development is more appropriate to understand as a strong regulatory and market signal rather than a fully settled enforcement outcome. The draft notice already identifies the direction of travel: imported ADB modules are being linked more closely to verifiable firmware security and auditability. At the same time, based on the information provided, detailed execution standards, review practice, and market response still require continued observation. That is why companies should distinguish between confirmed requirements in the draft and the final operational burden that may emerge later through implementation language, importer requests, or related technical documents.
How to read this development at the current stage
At this stage, the most rational reading is that the U.S. market is signaling a higher cybersecurity compliance threshold for imported ADB control modules. The immediate significance lies less in headline policy language and more in the likely effect on product selection, export readiness, documentation discipline, and supplier screening. It is more appropriate to understand this event as an important rule-development signal with concrete trade and compliance implications, while recognizing that the final execution path still needs to be tracked carefully.
Basis of this article and what still needs verification
This article is generated from the user-provided news title, event date, and event summary. For developments of this kind, relevant source types usually include official notices from regulators, trade or customs authorities, industry association updates, standards-related documents, and reporting from authoritative media. No specific official source link was provided in the input, so the exact source document path still needs continued verification. What should continue to be monitored includes later policy wording, compliance interpretation, certification or review expectations, changes in procurement documents, market feedback, and how companies implement the stated requirements in practice.