
Industry Portal
Related News
- 00
0000-00
ASPICE for Smart Optical Systems: Evidence Needed for Automotive Development - 00
0000-00
How to Select NVH Control Materials for Automotive Panels and Powertrain Systems - 00
0000-00
Choosing Low Rolling Resistance Tires for Longer Mileage and Lower Fleet Fuel Costs - 00
0000-00
Rain Sensing Systems Calibration: Methods for Reliable Detection and Testing - 00
0000-00
How to Evaluate a Photoelectric Sensing Supplier for Industrial Automation Projects
Tags
U.S. DOT ADB Cybersecurity Rule Proposal Opens Comment Window
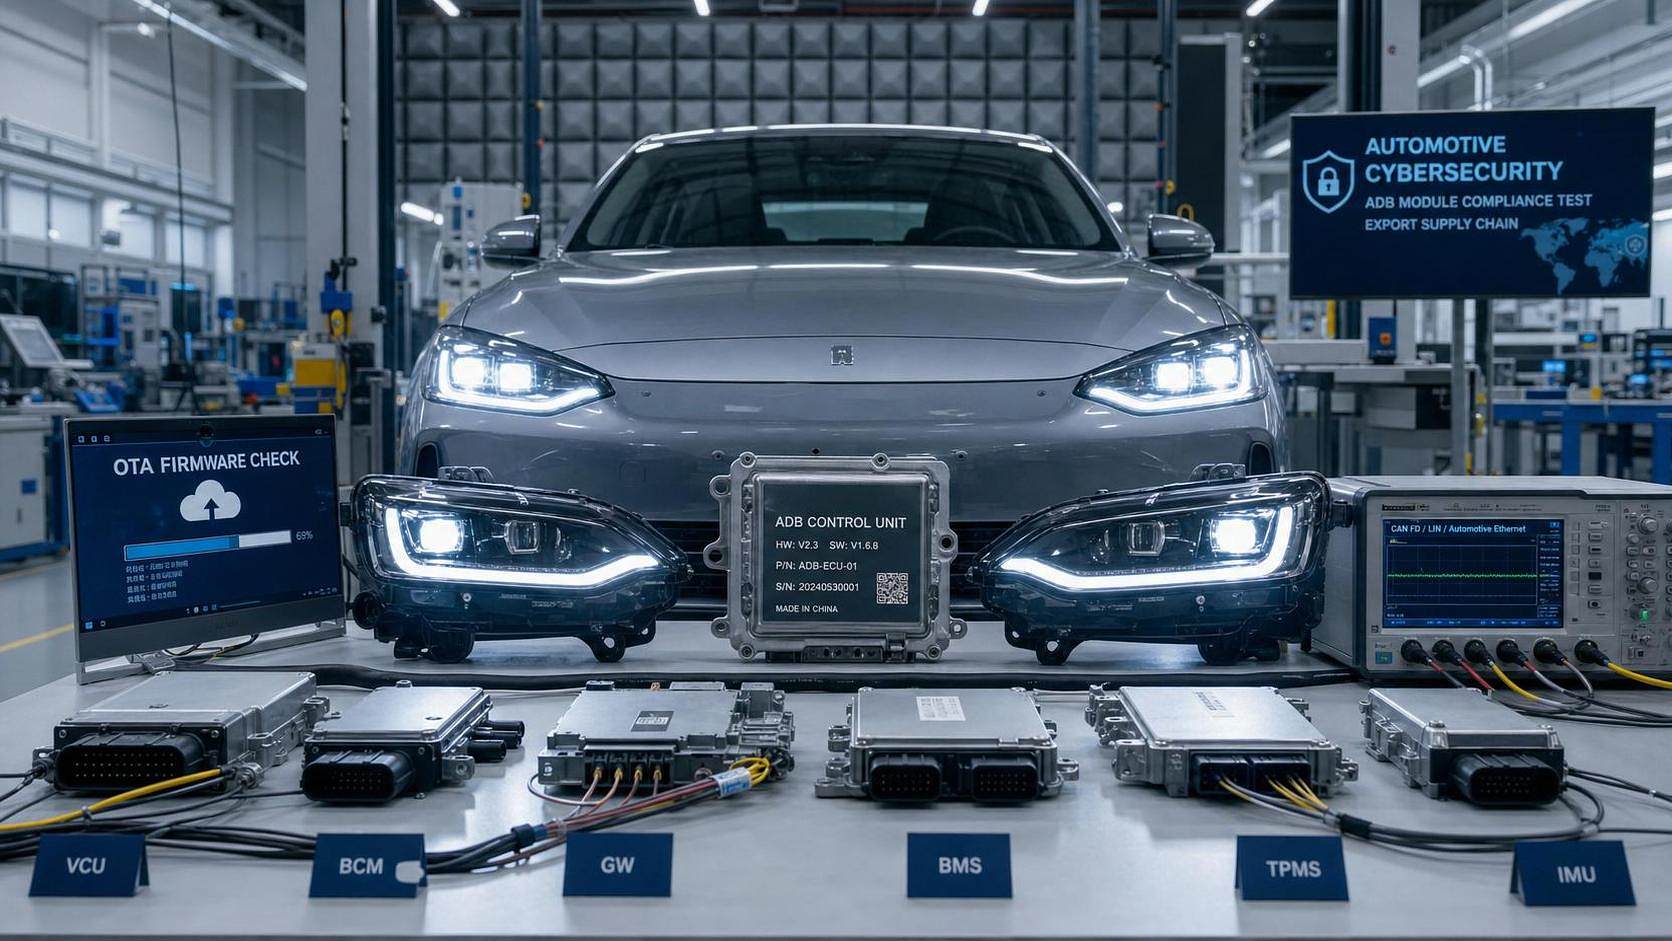
On June 27, 2026, NHTSA published a Federal Register proposal that would add FMVSS No. 135-A and set new cybersecurity requirements for vehicles equipped with adaptive driving beam (ADB) control modules. The proposal matters beyond a routine technical update because it connects product access, software development process control, and OTA firmware verification to a specific compliance path, with likely implications for exporters, module suppliers, vehicle manufacturers, certification preparation teams, and procurement decisions tied to ADB programs.
What the proposal formally puts on the table
According to the provided event summary, the U.S. Department of Transportation proposal was issued by NHTSA on June 27, 2026 through the Federal Register. It proposes a new FMVSS No. 135-A. The proposed rule would require all vehicles carrying ADB control modules to meet ISO/SAE 21434 cybersecurity development process requirements and OTA firmware security verification requirements. The title provided for the update also states that the comment period opens on July 1. The summary further indicates that the standard is expected to take effect in Q2 2027 and that Chinese ADB module exporters are likely to face added preparation around ASPICE certification and SOC2 compliance investment.
Where commercial and compliance pressure is likely to appear first
ADB module exporters may face a higher entry threshold
From an industry perspective, exporters of ADB control modules are among the most directly exposed groups because the proposal links market access more closely to cybersecurity development processes and firmware verification. The practical impact is likely to show up in customer qualification, technical document review, and pre-delivery compliance readiness. What deserves closer attention is whether export-facing suppliers can present development evidence, verification records, and supporting compliance materials in a form that buyers and downstream integrators can use in sourcing and homologation work.
Vehicle manufacturers and integrators may need tighter supplier screening
For vehicle manufacturers and system integrators using ADB modules, the rule change signals that supplier management may need to go beyond hardware performance and functional integration alone. Analysis shows that sourcing, platform planning, and delivery coordination could be affected if procurement teams begin to treat cybersecurity development process maturity and OTA security verification as mandatory supplier conditions. Even before final implementation, this kind of proposal can influence how technical specifications, supplier onboarding, and audit expectations are framed.
Certification and assurance service providers may see a shift in demand
Certification-related service providers, testing organizations, and compliance advisors may also be affected because the summary explicitly points to ASPICE preparation and SOC2-related investment pressure for Chinese ADB module exporters. Observably, that does not mean a confirmed enforcement model has already been set, but it does suggest that companies may start reviewing how software process evidence and control documentation align with customer and regulatory expectations tied to the proposed standard.
What companies should track before the rule is finalized
Review whether current development records can support ISO/SAE 21434 expectations
Analysis shows that companies involved in ADB module design, integration, or export should first examine whether existing cybersecurity development documentation is organized well enough to support an ISO/SAE 21434-based review. This is not yet the same as a confirmed final enforcement checklist, but it is a practical starting point for identifying documentation gaps that could later affect qualification or delivery.
Check how OTA firmware verification may change technical submissions
What deserves closer attention is the proposal's explicit reference to OTA firmware security verification. For affected businesses, this may influence how technical files, verification reports, internal approval records, and customer-facing submission packages are prepared. If bidding documents, purchasing specifications, or delivery acceptance criteria begin to reflect this direction, suppliers may need to adjust earlier than formal implementation.
Reassess certification budgeting and supplier readiness
The provided summary specifically mentions ASPICE preparation and SOC2 compliance investment for Chinese ADB module exporters. From a practical standpoint, companies may need to review budgeting assumptions, supplier qualification timelines, and internal ownership of compliance tasks. Since the input does not provide detailed enforcement mechanics, it is more appropriate to treat this as a preparation issue rather than a confirmed final cost outcome.
Watch for changes in customer requirements and delivery terms
Observably, proposals of this kind can affect business execution before the formal effective date if downstream customers begin updating technical requirements, onboarding conditions, or contract language. Exporters, procurement teams, and delivery managers should therefore track whether customer questionnaires, specification alignment work, or after-sales traceability expectations start to incorporate cybersecurity process evidence related to ADB modules.
Why this reads as an execution signal, but not yet a closed rule
Analysis shows that this development is best understood as more than a general policy discussion because it ties a specific vehicle function, ADB control modules, to named process and verification expectations. At the same time, it remains a proposal, and the title indicates that the comment period opens on July 1. It is therefore more appropriate to understand this as a meaningful execution signal with compliance and trade implications, while still recognizing that the final wording, implementation detail, and market response require continued observation.
How the market is likely to interpret the proposal for now
At this stage, the most balanced reading is that the proposal gives affected companies an early warning about where compliance expectations may tighten around ADB-related exports and supply relationships. It does not by itself confirm every downstream procurement rule or audit requirement, but it does indicate that cybersecurity process maturity and OTA verification could become more visible in qualification, certification preparation, and delivery planning. Current industry attention is therefore better directed toward readiness assessment and rule tracking than toward assuming that all execution details are already fixed.
Basis of this article and what still needs verification
This article is based on the user-provided news title, event date, and event summary. For developments of this type, relevant source categories usually include official regulatory notices, publications from supervisory agencies, trade or customs authority information, industry association updates, standard-setting documents, and reporting by authoritative media. A specific official source link was not provided in the input, so the exact publication text and later revisions still need to be verified on an ongoing basis. Further observation is also needed on the final rule language, implementation interpretation, certification expectations, tender document changes, market feedback, and how affected companies actually adjust compliance execution.