
Industry Portal
Related News
- 00
0000-00
How to Evaluate a Photoelectric Sensing Supplier for Industrial Automation Projects - 00
0000-00
Automatic Wipers for Buses: 7 Selection Criteria for Fleet Procurement - 00
0000-00
How Smart Optical Perception Prevents Collisions in Low-Light Driving Conditions - 00
0000-00
Private Label Tire Export: Evaluating Suppliers, Compliance, and Landed Cost - 00
0000-00
DOT-Compliant Truck Lighting: A Practical Guide to FMVSS 108 Requirements
Tags
US DOT Moves to Add OTA Checks to ADB Modules
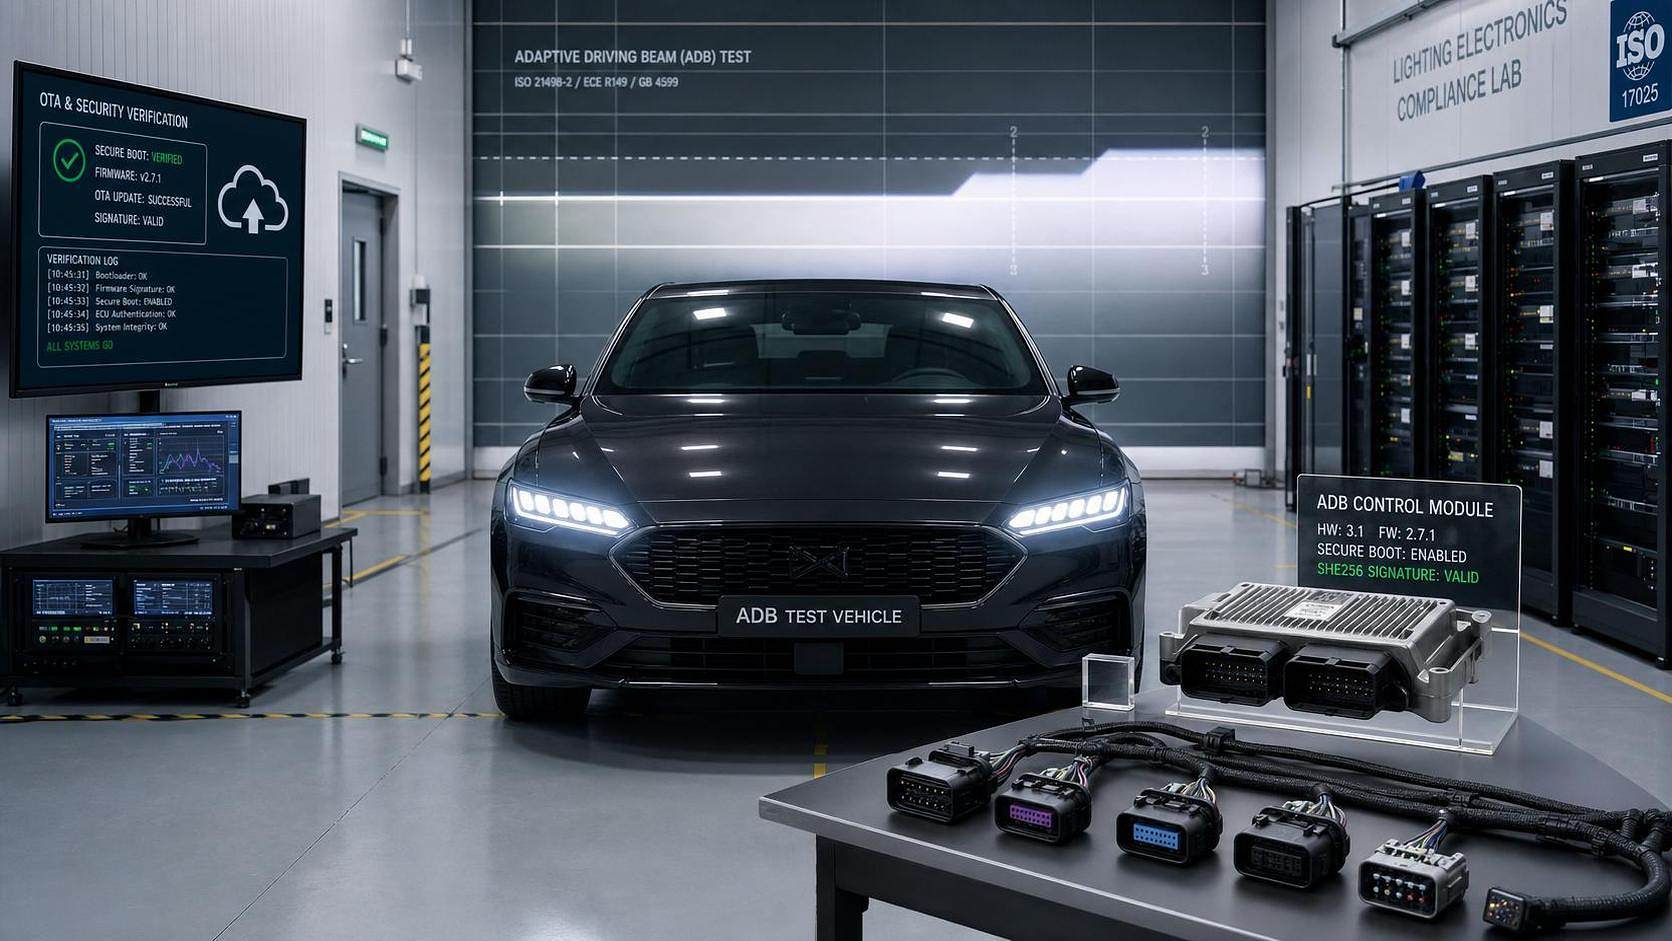
The timing of the underlying event is not explicitly stated in the provided information, but the policy signal is clear: on June 18, NHTSA issued a draft amendment to FMVSS No.108 that would add cybersecurity-oriented design requirements to vehicles with Adaptive Driving Beam (ADB) functions and to standalone ADB control modules. For manufacturers, exporters, certification-related service providers, and procurement teams connected to ADB products entering the U.S. market, this is worth close attention because it shifts part of market access from lighting performance alone toward firmware integrity, secure startup, and auditable operational records.
What the draft amendment would require
According to the provided summary, NHTSA released the FMVSS No.108 Amendment NPRM on June 18. The draft would require all vehicles equipped with ADB functionality, as well as standalone ADB control modules, to include Secure Boot, OTA firmware signature verification, and runtime event logging aligned with ISO/SAE 21434 compliance audit logging. The expected effective time stated in the input is Q2 2027. The same summary also indicates that the proposal is expected to affect the market-entry architecture design of ADB modules exported from China to the United States.
Where the compliance impact is likely to appear first
Export-facing ADB module suppliers
From an industry perspective, suppliers selling ADB control modules into the U.S. market may be affected because the proposed change reaches beyond optical or functional performance and into embedded security design. The main impact is likely to appear in product architecture, technical documentation, firmware management, and evidence prepared for customer or compliance review. What deserves closer attention is whether existing module platforms can support Secure Boot, signed OTA update verification, and audit-log retention without redesign.
Vehicle manufacturers and system integrators
For OEMs and integration partners, the proposed rule may affect sourcing specifications, validation workflows, and platform-level compliance alignment. Analysis shows that if ADB functionality and standalone control modules are both within scope, procurement and engineering teams may need to examine whether supplier submissions, interface definitions, and software update processes match the draft direction of FMVSS No.108. This is especially relevant where ADB capability is sourced from external module vendors rather than developed as a fully integrated in-house system.
Certification, testing, and compliance support functions
Certification-related firms, testing service providers, and internal compliance teams may also see changes in workload and focus. Observably, if runtime event logging and OTA signature verification become part of the compliance discussion, technical files, audit materials, and review checkpoints may need to reflect not only product function but also traceability and software authenticity controls. At this stage, however, the provided information does not define a final execution method, so these points are better understood as areas to monitor rather than settled requirements.
After-sales and traceability arrangements
For after-sales service and quality-traceability functions, the proposal may matter because OTA verification and event logging can affect how firmware updates, incident review, and service records are handled after shipment. Analysis shows that companies involved in U.S.-bound ADB products may need to pay closer attention to how update history and operational events are recorded and retrievable, especially if future compliance checks or customer requests begin to reference such records.
What companies should watch now
Check whether current designs already support the proposed controls
Companies tied to ADB products for the U.S. market should first review whether existing vehicle platforms or standalone modules already include Secure Boot, signed OTA verification, and runtime logging capabilities in a form that can be documented. If not, the key issue is not only technical addition but also whether redesign would affect validation timing, supplier coordination, or delivery planning.
Prepare technical and compliance files with software traceability in mind
What deserves closer attention is the quality of documents that may later be requested in customer reviews, compliance assessments, or certification-related processes. This may include firmware control descriptions, update verification logic, logging architecture summaries, and records that support auditability. Since the provided information does not include a final compliance template, companies should treat this as preparation for possible review expectations rather than a fixed document checklist.
Follow official wording and downstream procurement language
Analysis shows that the practical impact of the draft may emerge not only from the regulation itself but also from how downstream procurement specifications, tender documents, and supplier qualification requirements begin to reflect it. Exporters and component suppliers may therefore need to monitor both official rule development and any changes in customer-side technical specifications tied to ADB products for the U.S. market.
Review delivery, update, and support responsibilities across the supply chain
Where software integrity and event logging become part of product expectations, responsibilities between chip suppliers, module makers, vehicle manufacturers, and service teams may need clearer definition. Observably, firms should pay attention to who controls signing keys, who validates OTA packages, who retains logs, and how those responsibilities are reflected in supply agreements or delivery terms if the rule direction continues toward implementation.
Why this looks more like an execution signal than a finished rule
This development is more appropriate to understand as a regulatory direction with concrete design implications rather than as a fully settled compliance outcome. The reason is that the provided information describes a draft NPRM and an expected effective time, but it does not provide final enforcement detail, review procedures, or completed certification pathways. From an industry perspective, the significance lies in the signal that ADB-related market access may increasingly be assessed through both functional safety-related performance and software security controls.
How the market may need to interpret it for now
A rational reading of this update is that it raises the compliance threshold for ADB-related products entering the U.S. market without yet closing the discussion on execution details. For companies involved in exports, sourcing, compliance review, or technical delivery, the immediate value is in early alignment: identifying whether current module architecture, firmware governance, and traceability practices can support the direction described in the draft. At the current stage, it is more appropriate to treat this as a rule change under active development that warrants preparation and continued observation, rather than as a completed enforcement result.
Basis of this article and items still requiring verification
This article is generated from the user-provided title, event timing, and summary. The specific official source link was not provided in the input, so it still needs to be verified through ongoing review of materials such as regulator releases, official notices, standards-related documents, certification communications, trade or customs information, industry association updates, and reporting by authoritative media. Further observation is still needed on detailed policy wording, compliance interpretation, certification execution approaches, changes in procurement documents, market feedback, and how companies ultimately implement the proposed requirements in practice.