
Industry Portal
Related News
- 00
0000-00
Choosing Low Rolling Resistance Tires for Longer Mileage and Lower Fleet Fuel Costs - 00
0000-00
Rain Sensing Systems Calibration: Methods for Reliable Detection and Testing - 00
0000-00
How to Evaluate a Photoelectric Sensing Supplier for Industrial Automation Projects - 00
0000-00
Automatic Wipers for Buses: 7 Selection Criteria for Fleet Procurement - 00
0000-00
How Smart Optical Perception Prevents Collisions in Low-Light Driving Conditions
Tags
NHTSA Cybersecurity Guidance Raises ADB Supplier Entry Bar
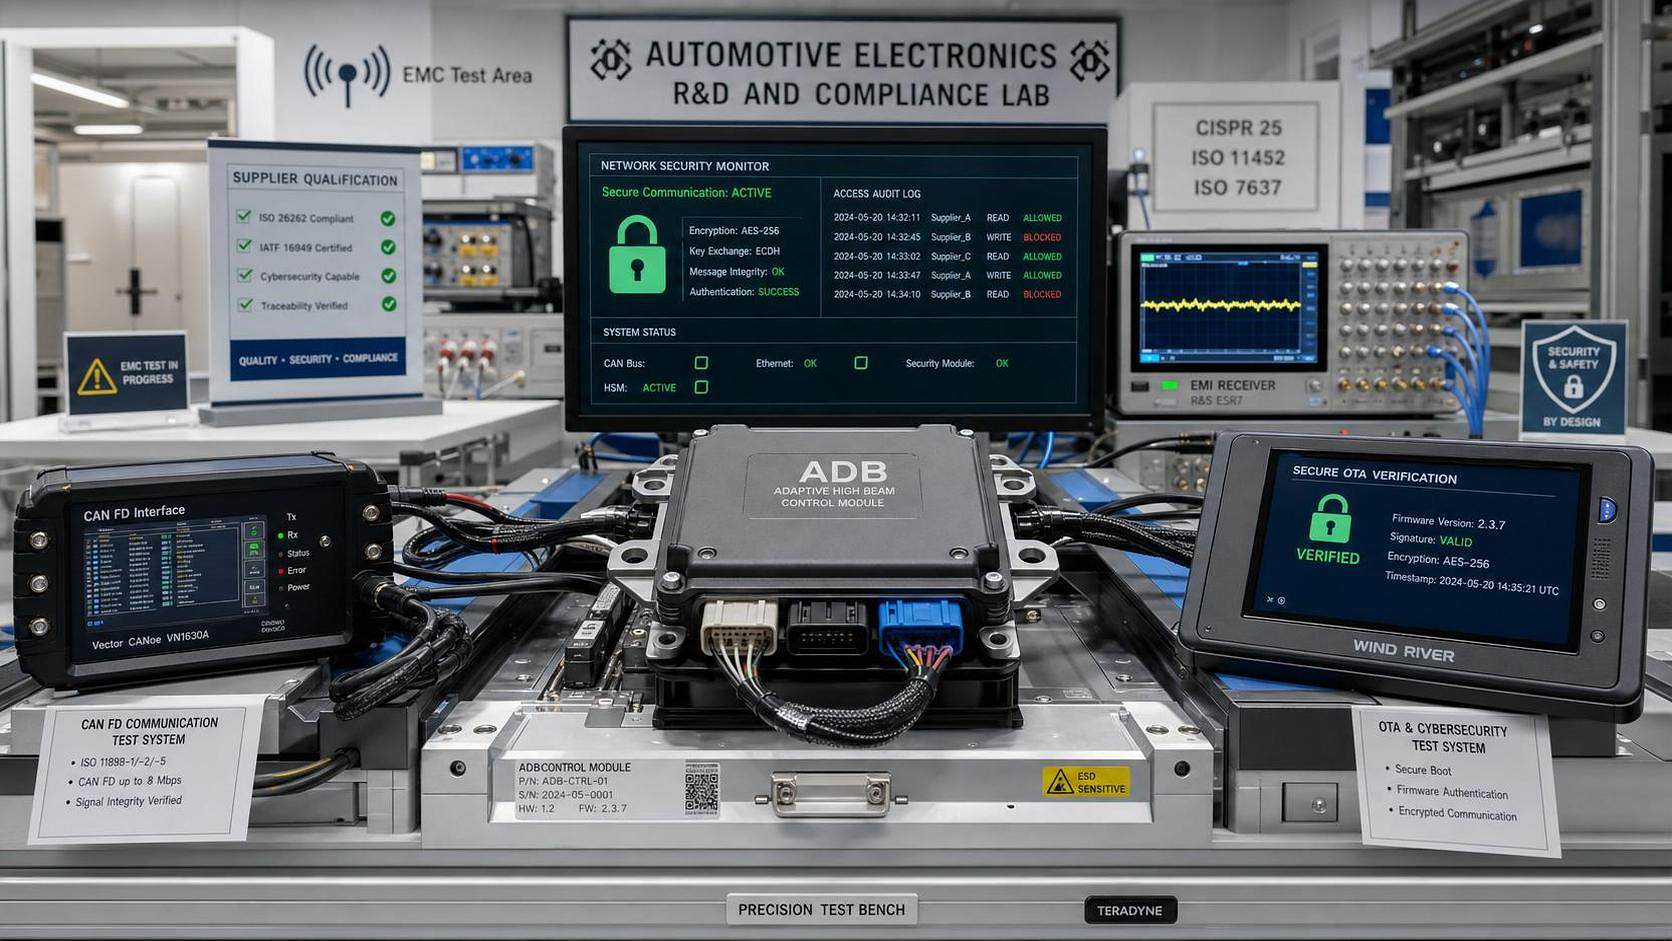
On July 9, 2026, the U.S. National Highway Traffic Safety Administration (NHTSA) released ADB Control Modules Cybersecurity Guidance v1.2, bringing new attention to how cybersecurity expectations are being translated into supplier access conditions for ADB control modules. The development matters not only because the guidance names OTA firmware update integrity checks, CAN FD communication encryption, and attack surface minimization design as mandatory assessment items, but also because those requirements have already been written into 2026 technical agreement appendices for tier-two suppliers by Ford, GM, and Tesla, creating direct implications for project qualification, export readiness, and delivery preparation for Chinese ADB control module exporters.
What the July 9 release explicitly changed
According to the information provided, NHTSA issued ADB Control Modules Cybersecurity Guidance v1.2 on July 9, 2026. The guidance, for the first time, lists three items as mandatory assessment points for ADB control modules: OTA firmware update integrity verification, CAN FD communication encryption, and attack surface minimization design.
The same information also states that the guidance itself is non-mandatory. However, Ford, GM, and Tesla have incorporated it into 2026 technical agreement appendices for tier-two suppliers. As a result, the change is already affecting project entry qualification for Chinese companies exporting ADB control modules.
How the rule shift reaches different business links
Project access is tightening at the export supplier level
From an industry perspective, Chinese ADB control module exporters are the most directly exposed group because the issue is no longer limited to policy awareness. Once the cybersecurity items appear in automaker technical agreement appendices, the impact moves into project access, supplier nomination, technical review, and bid alignment. What deserves closer attention is whether exporters can present documentation, design evidence, and verification materials that correspond to the newly emphasized assessment items.
Procurement and sourcing teams will face a different screening logic
For procurement functions at OEMs and upstream buyers, the practical effect is a shift in supplier screening criteria. Analysis shows that sourcing decisions may now depend not only on product performance and delivery capability, but also on whether a supplier can meet cybersecurity-related technical annex requirements tied to ADB control modules. This can affect technical clarification rounds, supplier qualification files, and contract attachments used during purchasing and nomination stages.
Engineering and manufacturing teams may see pressure on documentation and delivery readiness
For manufacturers and engineering teams, the pressure point is likely to appear in design review and delivery preparation. Observably, when OTA integrity verification, CAN FD encryption, and attack surface minimization are treated as mandatory assessment items in customer-facing technical documents, suppliers may need to align technical files, validation narratives, and compliance descriptions more closely with customer requirements. The immediate issue is less about public regulation in the abstract and more about whether deliverables can satisfy customer review gates.
Testing and compliance support providers may be pulled in earlier
Testing, certification-related, and compliance support organizations may also be affected because customers and exporters could require earlier evidence gathering around the three named cybersecurity items. Analysis shows that this may influence the timing and depth of technical document preparation, assessment support, and pre-delivery review, even where the underlying NHTSA guidance is not itself legally mandatory.
What companies should review now
Check whether customer appendices have turned guidance into a contract requirement
The first practical question is whether non-mandatory guidance has already become binding through customer technical agreements, purchasing terms, or supplier appendices. For companies serving U.S.-linked vehicle programs, that distinction matters because project qualification risk can arise from contractual adoption even when the original guidance is not a compulsory regulation.
Re-examine technical files against the three named assessment items
Companies should focus their internal review on the specific areas identified in the provided information: OTA firmware update integrity verification, CAN FD communication encryption, and attack surface minimization design. If existing bid files, compliance statements, design descriptions, or validation documents do not clearly address those points, the gap may appear during customer review or supplier onboarding.
Prepare for changes in bid documents and supplier qualification materials
Observably, one of the more immediate business impacts may come through technical bid documents and supplier qualification packages rather than through a standalone regulatory filing process. Exporters, procurement-facing teams, and program managers should therefore pay attention to revisions in annex language, technical checklists, and project-specific submission requirements tied to 2026 programs.
Watch execution signals rather than assume full market uniformity
Analysis shows that the current information supports close monitoring, but not blanket assumptions about identical implementation across all customers and projects. Companies should track how official wording, customer specifications, and review expectations develop in practice before treating all downstream requirements as fully standardized.
Why this looks more like an execution signal than a distant policy note
From an industry perspective, the most important feature of this development is the shift from guidance language to commercial enforcement through supplier technical appendices. That makes the event more than a policy update in name only. At the same time, it is more appropriate to understand this as a strong execution signal rather than a fully settled regulatory endpoint, because the provided information does not establish a complete public enforcement framework, uniform market practice, or detailed implementation path.
What deserves closer attention is how quickly customer-side procurement and engineering systems absorb these cybersecurity expectations into qualification checklists, technical clarifications, and delivery gates. Industry participants should also continue watching for changes in certification interpretation, tender documentation, and supplier review practice.
How the market should read this development for now
The current development is best read as a meaningful rise in project-entry compliance requirements for ADB control module suppliers involved in U.S.-linked business, especially where OEM technical appendices have already incorporated the NHTSA guidance. It does not automatically prove a fully mandatory regulatory regime across all channels, but it clearly signals that cybersecurity review is moving closer to procurement and supplier access decisions. A rational reading is that the rule change has already begun to affect execution at the customer and project level, while the broader market response and implementation detail still require continued observation.
Basis of this article and what still needs verification
This article is based on the user-provided news title, event date, and event summary. The analysis was generated from the stated facts that NHTSA released ADB Control Modules Cybersecurity Guidance v1.2 on July 9, 2026, that it introduced three mandatory assessment items for ADB control modules, and that Ford, GM, and Tesla incorporated the guidance into 2026 technical agreement appendices for tier-two suppliers.
For events of this type, relevant source categories usually include official regulatory announcements, regulator publications, trade or customs authority information, industry association updates, standards organization documents, and reporting by authoritative industry media. No specific official source link was provided in the input, so the exact official publication path still needs to be verified on an ongoing basis. It also remains necessary to monitor later policy detail, certification interpretation, changes in tender and technical documents, industry feedback, and actual company implementation.