
Industry Portal
Related News
- 00
0000-00
How to Specify Low-Pressure Casting Parts for Leak-Tight Automotive Housings - 00
0000-00
How to Specify an Electric Sunroof for Passenger Cars: Key Design and Safety Factors - 00
0000-00
North American Vehicle Aesthetics: Trends Shaping Exterior Design and Materials - 00
0000-00
ASPICE for Smart Optical Systems: Evidence Needed for Automotive Development - 00
0000-00
How to Select NVH Control Materials for Automotive Panels and Powertrain Systems
Tags
EU Sets Cybersecurity Rules for ADB Modules
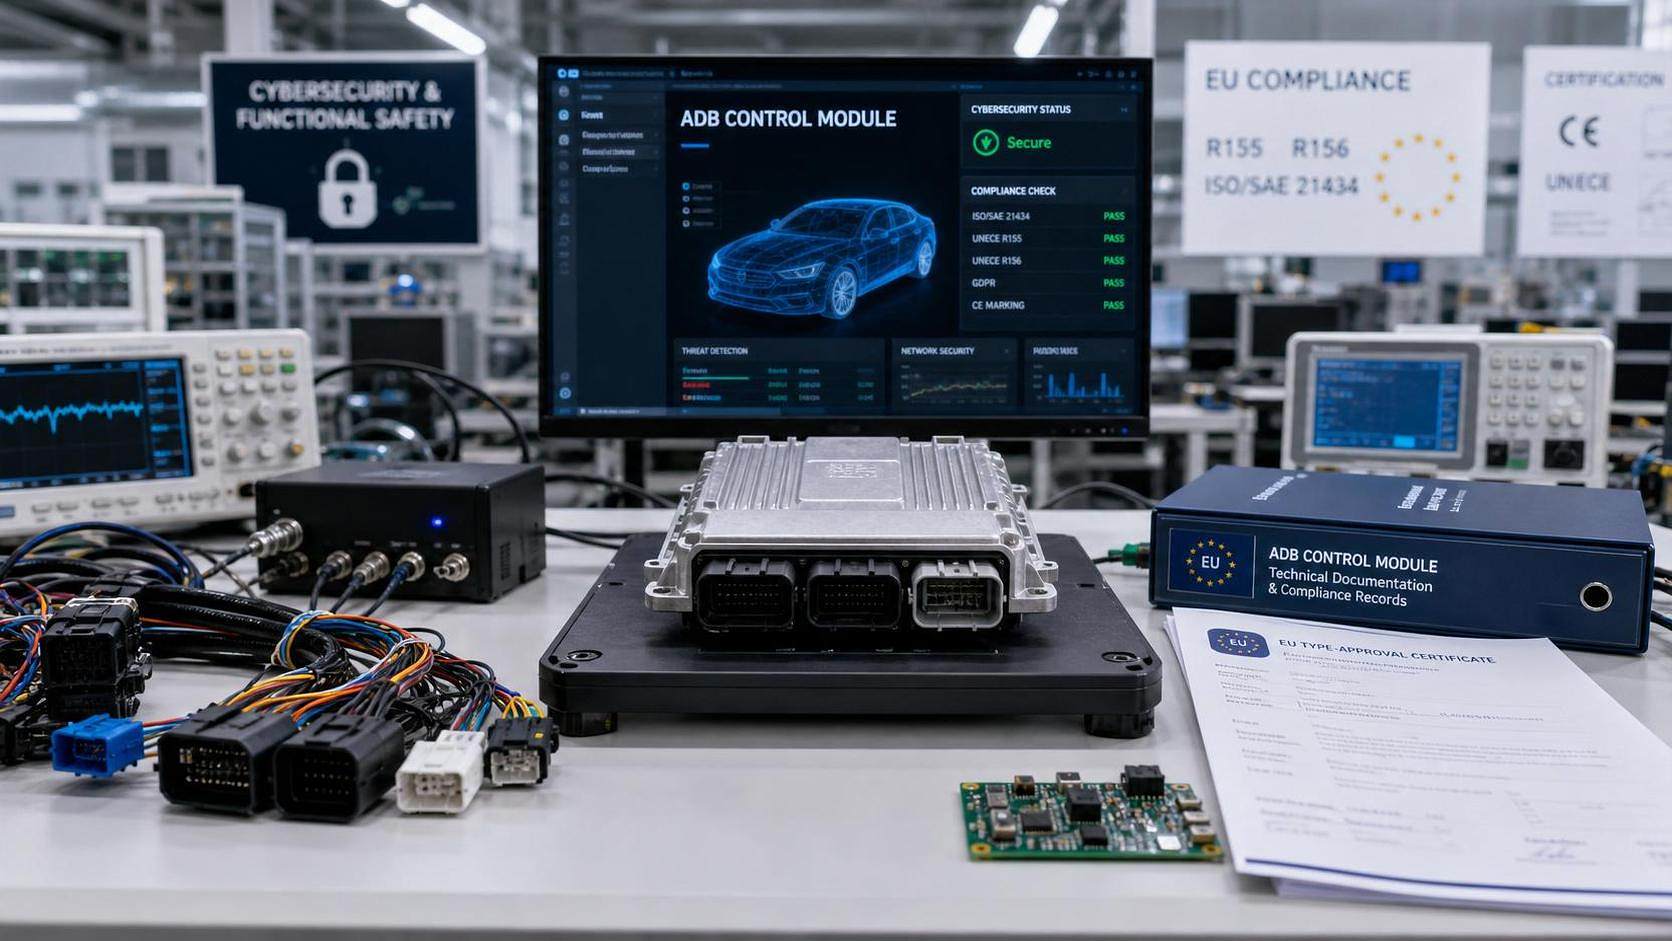
On 14 July 2026, the European Commission formally adopted Regulation (EU) 2026/1289, setting new cybersecurity requirements for ADB Control Modules placed on the EU market after 1 October 2026. For companies involved in exporting, certifying, and integrating these modules, especially Tier 2 and Tier 3 suppliers shipping from China, the development matters because it links market access more closely to cybersecurity management, threat analysis, and approval documentation timing.
What the regulation now requires
According to the information provided, Regulation (EU) 2026/1289 requires all ADB Control Modules placed on the EU market after 1 October 2026 to be covered by UNECE R155-compliant cybersecurity management systems (CSMS) and threat analysis aligned with ISO/SAE 21434. The same information indicates that affected suppliers will need pre-market CSMS audits and updates to type-approval documentation. It also states that these added steps are expected to extend certification timelines by around six to eight weeks.
Where the immediate pressure is likely to appear
Export-oriented module suppliers face earlier compliance pressure
From an industry perspective, the most direct impact falls on Tier 2 and Tier 3 suppliers exporting ADB modules from China to the EU market. The reason is straightforward: the new rule is tied to whether a product can be placed on the market, so cybersecurity readiness becomes part of the commercial path, not only a technical afterthought. The main pressure points are likely to be audit preparation, internal process alignment, and completion of approval-related documents before shipment or launch milestones.
Certification and approval work will need tighter scheduling
Analysis shows that teams responsible for homologation, compliance coordination, and customer submissions may feel the impact through timing rather than through product specification alone. If pre-market CSMS audits and type-approval updates add roughly six to eight weeks, certification planning, sample release timing, and customer-facing delivery commitments may all need closer coordination.
Downstream customers may pay more attention to supplier readiness
Observably, customers sourcing ADB Control Modules for EU programs may need to watch not only product performance but also whether suppliers can support the required cybersecurity evidence. In practical terms, procurement and program teams may place greater attention on documentation status, audit preparedness, and whether certification timing could affect sourcing decisions or launch schedules.
What companies should review now
Check whether current CSMS evidence is sufficient for EU placement
What deserves closer attention is whether existing cybersecurity management materials are already aligned with UNECE R155 expectations for the ADB Control Modules concerned. The regulation does not merely suggest better internal control; it introduces a market-entry condition for products placed on the EU market after the stated date.
Reassess documentation readiness for type approval
Companies involved in EU-bound ADB modules should review whether their current type-approval files can be updated without delaying customer programs. Based on the information provided, documentation updates are not a side issue but part of the direct compliance workload created by the new rule.
Adjust certification timelines in customer and internal planning
Analysis shows that the reported six-to-eight-week extension should be treated as a planning input, especially for businesses working on tight export schedules. Sales, compliance, and delivery teams may need a more conservative timeline assumption when discussing quotations, production windows, and project milestones tied to the EU market.
Separate regulatory wording from execution risk
From an industry perspective, one practical point is to distinguish between the formal adoption of the rule and the difficulty of executing against it. The regulation is a confirmed development, but the operational challenge for each company will depend on how quickly audit preparation, threat analysis alignment, and approval updates can be organized into normal business processes.
Why this matters beyond a single compliance update
As an editorial observation, this development is better understood as more than a short-term paperwork change. The confirmed facts already show that cybersecurity expectations are being tied directly to market access for a defined product category. At the same time, it is still more appropriate to view the broader commercial effect as something that will become clearer through implementation, especially in how suppliers absorb the added audit and approval workload.
How to read the signal at this stage
At this stage, the industry significance lies in the fact that cybersecurity compliance for ADB Control Modules is moving into a formal pre-market requirement for the EU. The immediate result is clear in procedural terms: additional audits, updated documentation, and longer certification lead times. The broader business impact should be read cautiously as a concrete regulatory shift with operational consequences, rather than as a complete reshaping of the supply chain.
Basis of this article and points to keep verifying
This article is based on the user-provided news title, event date, and event summary. For developments of this kind, relevant source types typically include official regulatory announcements, company disclosures, industry association updates, authoritative media coverage, and standards-related documents. A specific official source link was not provided in the input, so the exact publication trail still needs continued verification. Follow-up attention should remain on any subsequent official wording, implementation details reflected in approval practice, and how certification timing is handled in actual supply arrangements.