
Industry Portal
Related News
- 00
0000-00
ASPICE for Smart Optical Systems: Evidence Needed for Automotive Development - 00
0000-00
How to Select NVH Control Materials for Automotive Panels and Powertrain Systems - 00
0000-00
Choosing Low Rolling Resistance Tires for Longer Mileage and Lower Fleet Fuel Costs - 00
0000-00
Rain Sensing Systems Calibration: Methods for Reliable Detection and Testing - 00
0000-00
How to Evaluate a Photoelectric Sensing Supplier for Industrial Automation Projects
Tags
EU R155 CSMS Upgrade: ADB Control Modules Require Cybersecurity Pen Testing
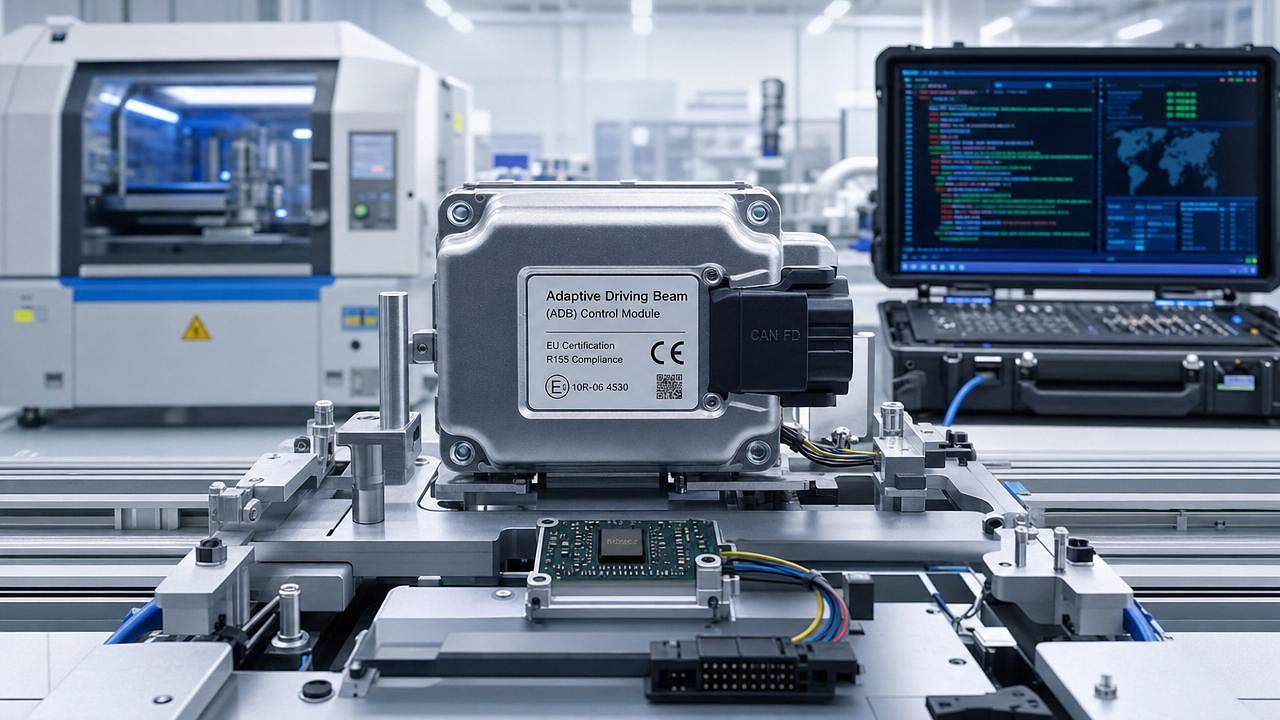
Brussels, 2024 — A major regulatory shift is set to reshape the global automotive lighting supply chain: effective 1 October 2026, all Adaptive Driving Beam (ADB) control modules exported to the European Union must comply with an upgraded cybersecurity requirement under UNECE Regulation No. 155’s Cyber Security Management System (CSMS) framework. The mandate — confirmed by TÜV Rheinland Germany in its 14 May 2026 compliance guidance — introduces mandatory third-party cybersecurity penetration testing, attack surface mapping, and OTA firmware signature validation for every ADB control module. This affects Chinese OEMs and Tier 1 suppliers most directly, triggering implications across certification timelines, export readiness, and compliance cost structures.
Event Overview
On 14 May 2026, TÜV Rheinland Germany published updated regulatory guidance clarifying that, from 1 October 2026 onward, all ADB control modules placed on the EU market must be certified under UNECE R155 with a fully implemented and audited CSMS — including successful completion of independent, accredited cybersecurity penetration testing. Submission of documented attack surface mapping and evidence of secure over-the-air (OTA) firmware signing verification is now a formal prerequisite for type approval. No transitional grace period is specified for new applications submitted after the deadline.
Industries Affected
Direct Exporters (OEMs & Tier 1 Suppliers)
Chinese automotive OEMs and Tier 1 suppliers exporting ADB control modules to the EU face immediate impact on product launch scheduling and homologation budgets. Because penetration testing must be conducted on final hardware-software configurations — not prototypes or development builds — design freeze timelines are effectively accelerated. Certification lead times are projected to extend by 8–12 weeks per module variant, and test costs (including retesting after any software update) may rise by 30–45% compared to prior R155 audits.
Raw Material & Component Procurement Firms
Suppliers of microcontrollers, secure elements (e.g., HSMs), cryptographic libraries, or OTA-enabling communication modules must now align technical documentation and security claims with R155 CSMS evidence requirements. Procurement contracts increasingly stipulate traceable attestation of cryptographic agility, secure boot integrity, and vulnerability disclosure responsiveness — capabilities previously treated as optional enhancements rather than compliance prerequisites.
Manufacturing & Integration Facilities
Electronics manufacturing services (EMS) and system integrators handling final assembly, flashing, and calibration of ADB modules must demonstrate controlled production environments compliant with CSMS-controlled change management. This includes logging firmware signing keys usage, validating build-chain integrity, and retaining audit-ready records of all OTA update packages deployed during production — extending quality assurance workflows beyond traditional ISO/TS 16949 scope.
Supply Chain & Certification Support Providers
Regulatory consultancies, test laboratories, and CSMS implementation partners are experiencing surging demand for cross-functional teams fluent in both automotive functional safety (ISO 26262) and cybersecurity engineering (ISO/SAE 21434). Notably, only labs accredited under ILAC-MRA with specific R155 penetration testing scope may issue accepted reports — narrowing the pool of viable service providers and increasing booking lead times.
Key Focus Areas & Recommended Actions
Initiate CSMS Gap Assessment Before Q3 2025
Organizations should commission a formal CSMS maturity review against UN R155 Annex 5 criteria — especially Sections 5.2 (risk assessment methodology), 5.3 (incident response), and 5.4 (secure development lifecycle). Delaying this until 2026 risks insufficient time to remediate process-level gaps before penetration testing begins.
Prioritize Attack Surface Documentation Early
Attack surface mapping — covering interfaces (CAN FD, Ethernet, BLE), external dependencies (cloud APIs, OTA servers), and physical access points — must be finalized *before* penetration testing commences. Teams should treat this as a living document updated with each software release, not a one-time deliverable.
Validate OTA Signing Infrastructure Against ETSI EN 303 645
Firmware signing must meet minimum cryptographic strength (e.g., ECDSA with P-384 or RSA-3072), key lifecycle governance (HSM-backed key storage, rotation policies), and signature verification logic embedded in bootloader code. Third-party labs will verify both the signing process *and* the target device’s runtime enforcement capability.
Editorial Perspective / Industry Observation
Observably, this requirement signals a structural shift — not merely a technical checkbox — in how regulators assess automotive cybersecurity. Unlike earlier interpretations of R155 that emphasized process documentation, the 2026 mandate demands empirical, adversarial validation of real-world resilience. Analysis shows that fewer than 20% of currently certified Chinese ADB suppliers have publicly disclosed penetration test reports meeting ETSI or ISO/IEC 18045 benchmarks. From an industry perspective, the tighter linkage between OTA architecture and regulatory acceptance also accelerates consolidation among smaller Tier 2 suppliers lacking dedicated cybersecurity engineering capacity.
Conclusion
This regulatory evolution underscores a broader trend: cybersecurity is no longer a post-development add-on but a foundational element of automotive product definition. For exporters targeting the EU, compliance readiness must begin at architecture design — not at the certification gate. A measured, phased investment in CSMS infrastructure today reduces both time-to-market risk and long-term compliance overhead tomorrow.
Source Attribution
Official guidance issued by TÜV Rheinland Germany, dated 14 May 2026 (Document Ref: TR-GL-R155-CSMS-ADB-2026-05). Referenced against UNECE Regulation No. 155 (Rev. 4, 2023) and Supplement 12 (Cybersecurity Audit Protocol). Note: Final interpretation of ‘ADB control module’ scope — particularly regarding integration boundaries with ADAS domain controllers — remains subject to ongoing clarification by the WP.29 GRVA working group; updates expected Q4 2025.