
Industry Portal
Related News
- 00
0000-00
How to Evaluate a Photoelectric Sensing Supplier for Industrial Automation Projects - 00
0000-00
Automatic Wipers for Buses: 7 Selection Criteria for Fleet Procurement - 00
0000-00
How Smart Optical Perception Prevents Collisions in Low-Light Driving Conditions - 00
0000-00
Private Label Tire Export: Evaluating Suppliers, Compliance, and Landed Cost - 00
0000-00
DOT-Compliant Truck Lighting: A Practical Guide to FMVSS 108 Requirements
Tags
EU ECE R155 CSMS Update: ADB Control Modules Require Cybersecurity Penetration Testing
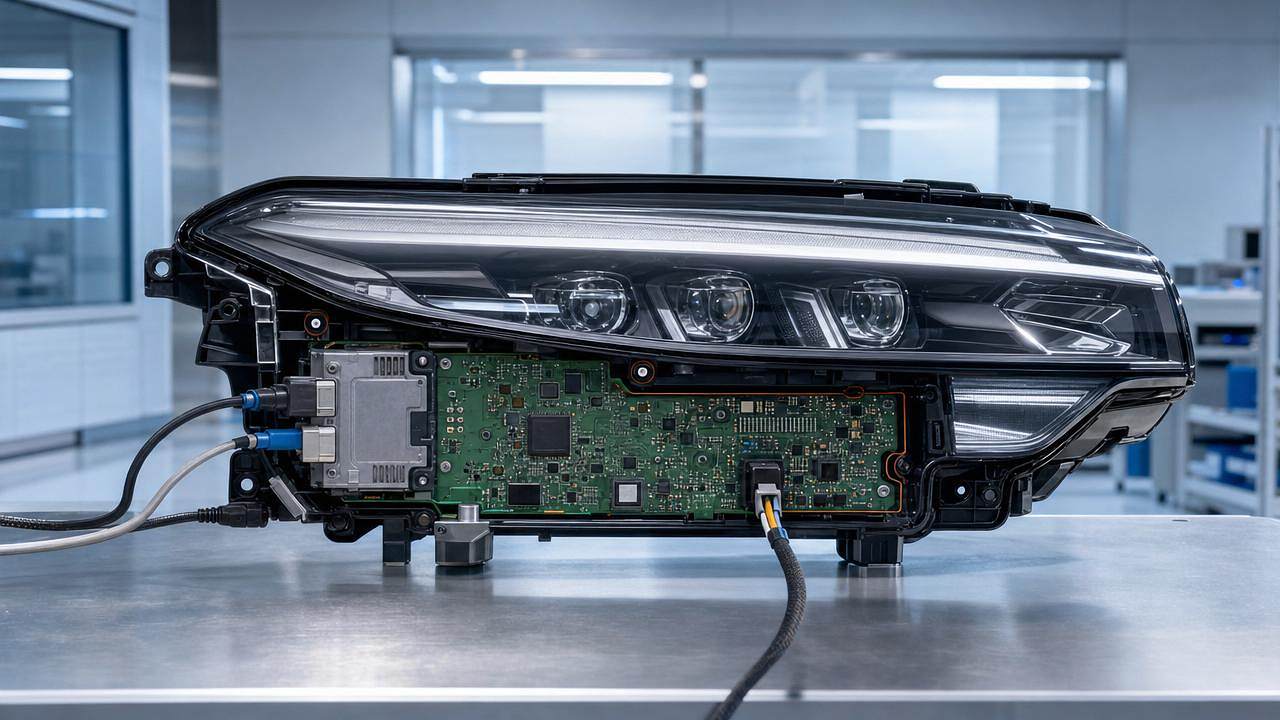
On May 11, 2026, the United Nations Economic Commission for Europe (UNECE) updated its implementation guidelines for Regulation ECE R155, mandating that all newly submitted Adaptive Driving Beam (ADB) Control Modules undergo third-party cybersecurity penetration testing per ISO/SAE 21434. This requirement directly affects manufacturers and exporters of ADB controllers targeting the EU vehicle market — particularly those based in China — and signals a tightening of cybersecurity compliance for automotive electronic systems.
Event Overview
On May 11, 2026, UNECE issued an update to the ECE R155 regulation implementation guidance. The update specifies that any new type-approval application for ADB Control Modules must include cybersecurity penetration test reports conducted by accredited third-party organizations (e.g., TÜV Rheinland, SGS). The testing scope explicitly covers the CAN FD communication protocol stack and the Over-the-Air (OTA) software update module. Chinese manufacturers exporting ADB controllers to the EU must complete such testing by Q3 2026; failure to do so will result in loss of eligibility for EU new vehicle type approval.
Which Subsectors Are Affected
Direct Exporters (OEM Suppliers & Tier-1s)
Manufacturers that supply ADB Control Modules directly to EU-based vehicle OEMs or apply for EU type approval under their own name are subject to immediate compliance obligations. Their products cannot proceed through certification unless test evidence is submitted before the Q3 2026 deadline.
Contract Manufacturers & EMS Providers
Electronics manufacturing service (EMS) providers producing ADB modules on behalf of foreign or domestic clients must now incorporate cybersecurity validation into their development and release workflows. Absence of penetration test readiness may delay production ramp-up or trigger contractual requalification requirements.
Automotive Cybersecurity Testing Service Providers
Accredited labs and cybersecurity validation firms (e.g., TÜV Rheinland, SGS) face increased demand for ISO/SAE 21434-aligned penetration testing focused specifically on CAN FD and OTA components. Capacity planning and test protocol alignment with UNECE’s updated expectations become operationally critical.
Export Compliance & Certification Consultants
Firms supporting Chinese exporters with EU regulatory navigation must update their guidance to reflect the mandatory inclusion of penetration test reports in CSMS (Cybersecurity Management System) documentation packages. This affects audit checklists, gap assessments, and timeline planning for R155 applications.
What Relevant Companies or Practitioners Should Focus On and How to Respond
Monitor official UNECE and EU national type-approval authority updates
The May 11, 2026 guidance is an implementation update — not a full regulatory amendment. Stakeholders should track whether further technical clarifications (e.g., minimum test depth, acceptable vulnerability thresholds, or exemptions for legacy modules) are published by UNECE Working Party GRVA or national authorities such as KBA (Germany) or RDW (Netherlands).
Prioritize modules with CAN FD and OTA functionality for immediate validation planning
Only ADB Control Modules incorporating CAN FD communication and/or OTA update capability fall under this specific mandate. Companies should inventory current product families, identify which models meet both criteria, and allocate testing resources accordingly — rather than applying blanket validation across all ADB variants.
Distinguish between CSMS process compliance and technical test execution
ECE R155 requires a functioning Cybersecurity Management System, but this update adds a discrete technical verification step. Firms must ensure that penetration testing is treated as a distinct deliverable — not conflated with broader CSMS audits or functional safety assessments (e.g., ISO 26262).
Initiate engagement with accredited test labs ahead of Q3 2026
Lead times for ISO/SAE 21434 penetration testing — especially for embedded automotive systems with complex communication stacks — often exceed 8–12 weeks. Exporters should secure lab capacity and align test scoping documents (e.g., threat modeling inputs, attack surface definitions) no later than June 2026.
Editorial Perspective / Industry Observation
Observably, this update reflects a shift from high-level process assurance (CSMS) toward concrete, protocol-specific technical validation within ECE R155 enforcement. Analysis shows it is less a standalone policy change and more a calibration of existing requirements — tightening interpretation around what constitutes sufficient evidence of cybersecurity resilience for ADAS-critical components. From an industry perspective, it signals that regulatory authorities are increasingly treating cybersecurity not as a documentation exercise, but as a verifiable engineering outcome. Current monitoring should focus less on whether the rule applies, and more on how consistently and transparently national type-approval bodies enforce the updated expectation across different module architectures and supplier tiers.
This is not yet a de facto market barrier — but it is a binding procedural checkpoint for new certifications. Continued observation is warranted for evidence of retroactive application or extension to other ADAS control units beyond ADB modules.
Conclusion
Ultimately, this update formalizes a technical compliance prerequisite for ADB Control Modules entering the EU market. It does not introduce new regulatory architecture, but elevates the evidentiary bar for cybersecurity validation. For affected stakeholders, the situation is best understood not as an emergency, but as a defined, time-bound integration task within established R155 and ISO/SAE 21434 frameworks. Proactive scoping, lab coordination, and precise alignment with the CAN FD + OTA scope remain the most effective near-term responses.
Information Sources
Main source: United Nations Economic Commission for Europe (UNECE), ECE R155 Implementation Guidance Update, issued May 11, 2026.
Ongoing observation required for: National type-approval authority interpretations (e.g., KBA, RDW), potential extensions to other ADAS modules, and clarification on test report acceptance criteria.